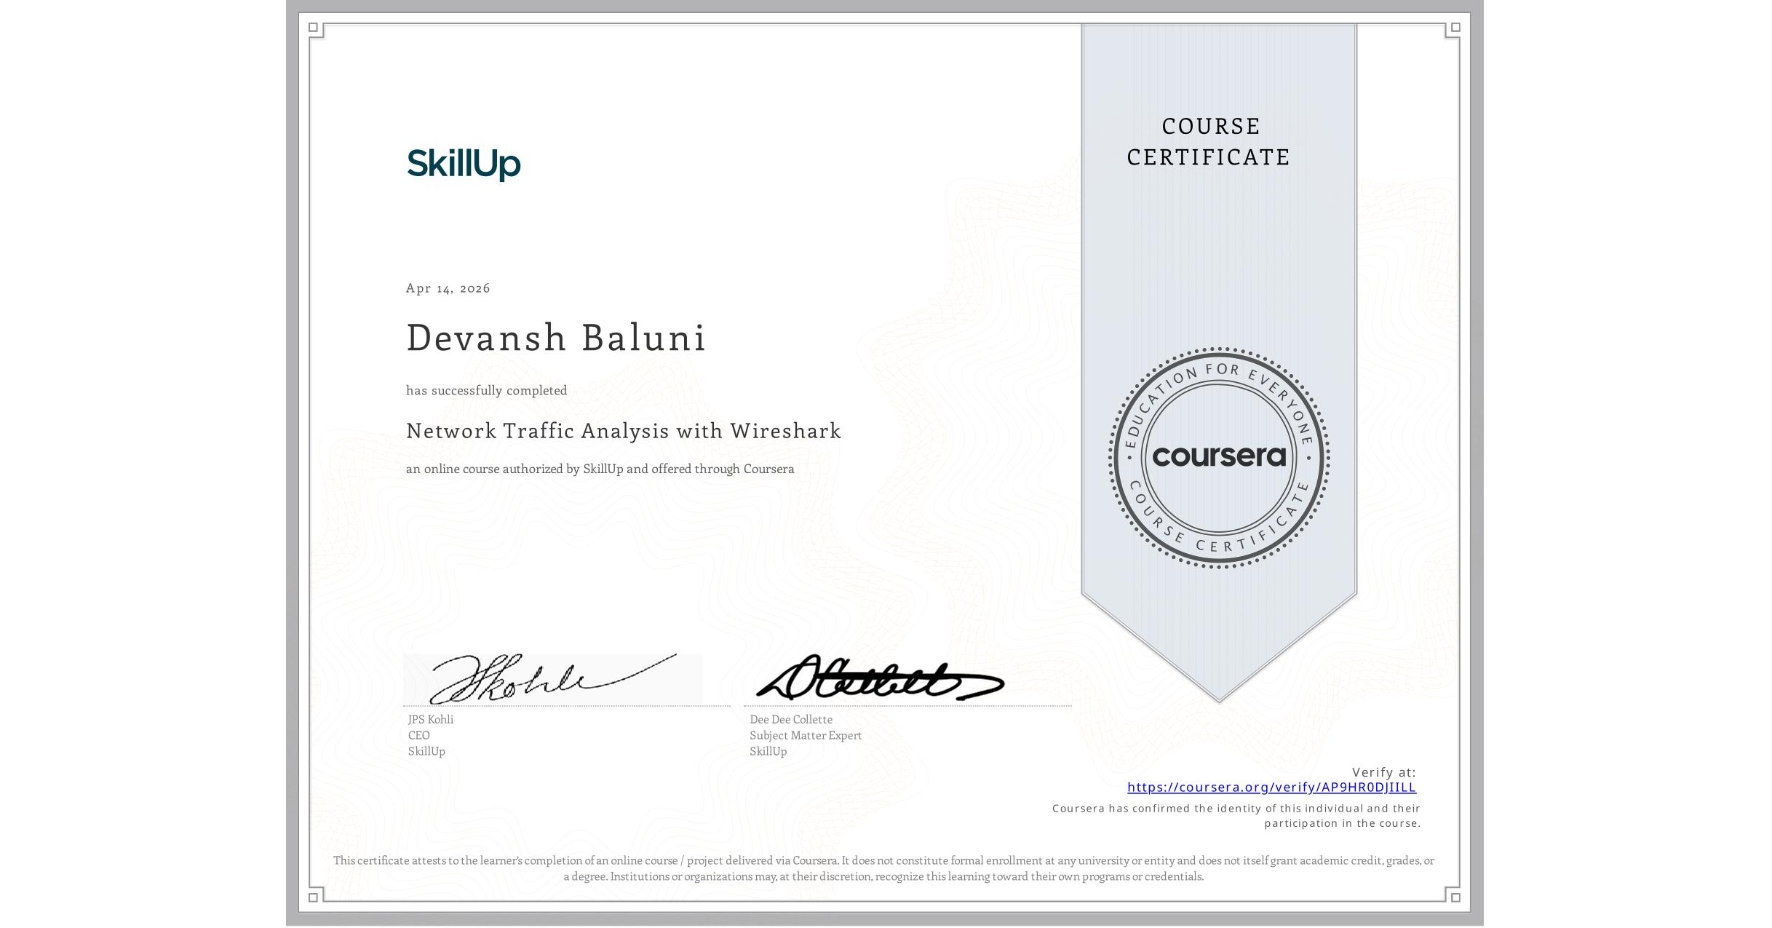
Network Traffic Analysis with Wireshark
Completed by Devansh Baluni
April 14, 2026
12 hours (approximately)
Devansh Baluni's account is verified. Coursera certifies their successful completion of Network Traffic Analysis with Wireshark

What you will learn
Describe the principles, objectives, tools, and challenges of network forensics and traffic analysis.
Apply packet capture and filtering techniques using tools like Wireshark.
Analyze network protocols and traffic using Deep Packet Inspection (DPI) and flow data to identify potential security threats.
Create detailed reports from captured data tailored for stakeholders and incident response teams.
Skills you will gain
- Category: Network Analysis
- Category: Computer Security
- Category: Incident Response
- Category: Anomaly Detection
- Category: Technical Communication
- Category: Network Security
- Category: Cybersecurity
- Category: Network Protocols
- Category: Digital Forensics
- Category: Threat Detection
- Category: Network Monitoring
- Category: Distributed Denial-Of-Service (DDoS) Attacks