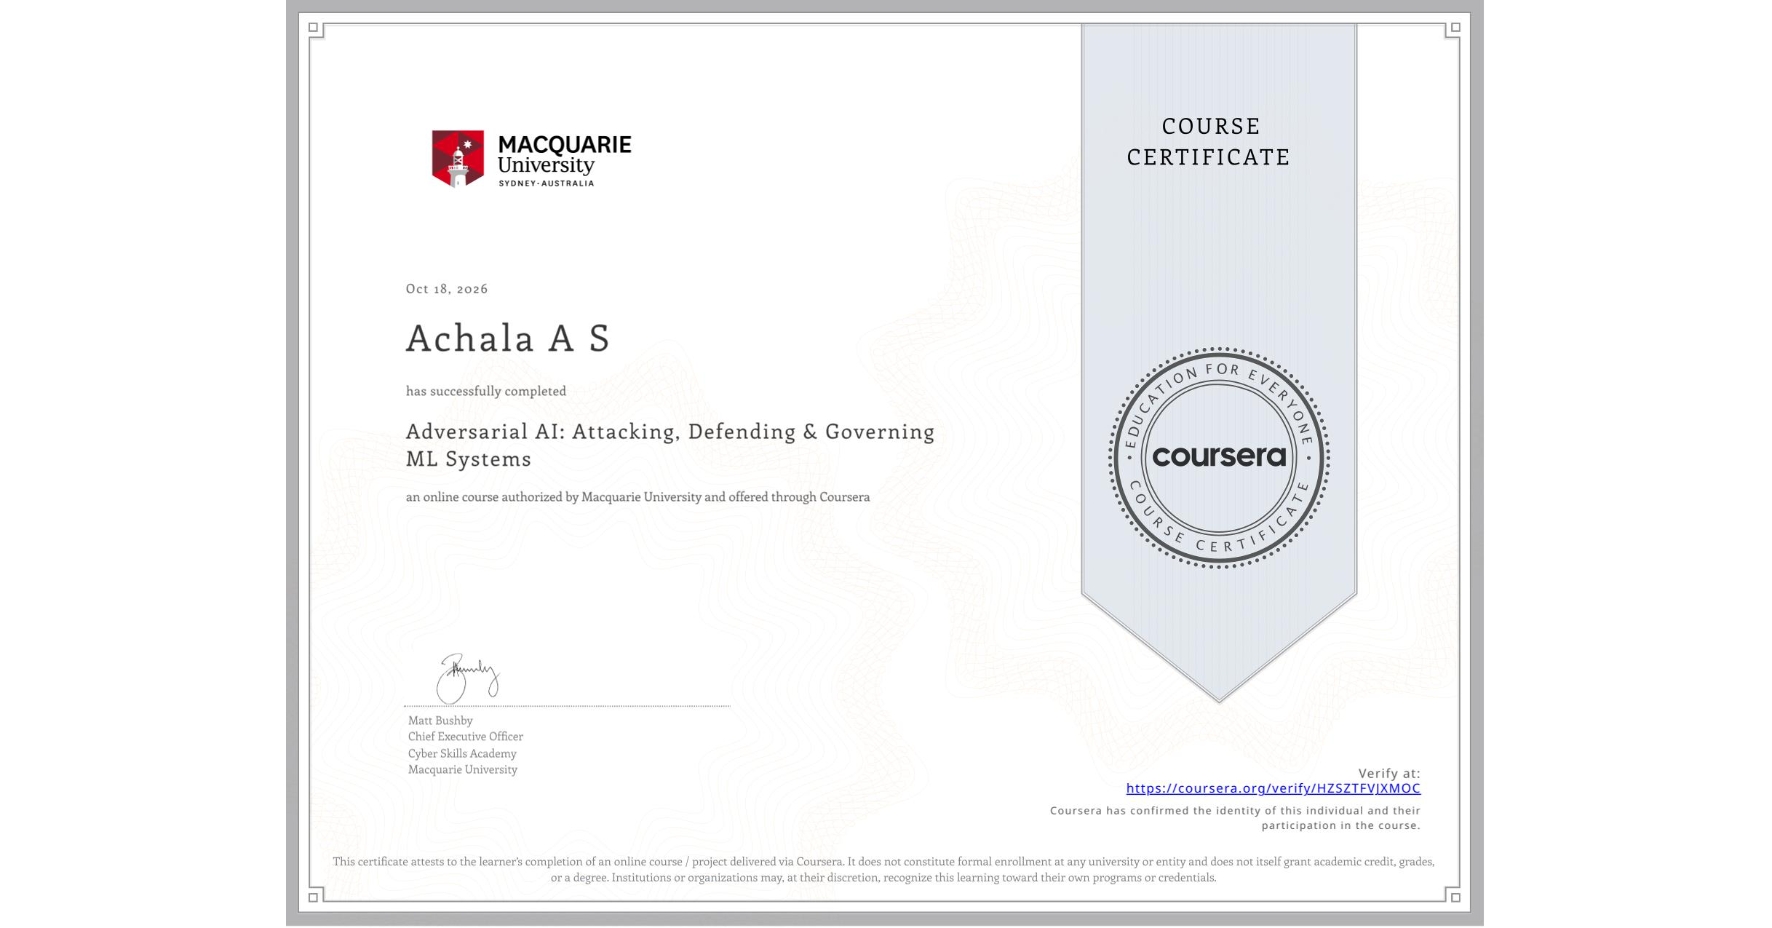
Adversarial AI: Attacking, Defending & Governing ML Systems
Completed by Achala A S
October 18, 2026
10 hours (approximately)
Achala A S's account is verified. Coursera certifies their successful completion of Adversarial AI: Attacking, Defending & Governing ML Systems

What you will learn
Analyse adversarial attack vectors targeting ML systems including poisoning, model stealing, & backdoor exploits, and assess their operational impact
Design & implement layered technical defences using differential privacy, guardrail protection, & secure algorithm design to maintain model integrity
Plan and conduct AI security testing using red, purple, and blue teaming approaches to validate ML model robustness under adversarial conditions
Evaluate responsible AI governance frameworks and regulatory requirements to ensure AI systems are ethical, fair, and compliant
Skills you will gain
- Category: Responsible AI
- Category: Artificial Intelligence and Machine Learning (AI/ML)
- Category: AI Security
- Category: Data Governance
- Category: Penetration Testing
- Category: Cybersecurity
- Category: Information Privacy
- Category: Cyber Governance
- Category: Artificial Intelligence
- Category: Cyber Attacks
- Category: Regulatory Compliance
- Category: Data Ethics